
The immediate problem
Companies across Madrid, Seoul, and beyond are seeing a clear issue: consumer devices and M2M fleets rely on weak SIM management that invites fraud and downtime. Vendors that sell sim card solutions can help, but many providers still treat security like an afterthought. The result is exposed credentials, brittle OTA provisioning flows, and avoidable bill shocks for customers who expect privacy and reliability. Engineers and product managers call this out—now it’s a procurement problem, not just a dev problem. Terms like SIM, secure element, and eSIM get tossed around, but the core gap is consistent, auditable hardware trust.
Why Europe and Asia feel the pressure
Regulation and market expectations collide. European firms face GDPR scrutiny and audit obligations that push them toward stronger cryptographic custody on the device. Asian telcos demand fast onboarding and tight fraud controls for massive IoT rollouts. Mobile World Congress in Barcelona and similar industry meetups made that clear last year—vendors showed solutions, but customers asked for measurable proofs. That’s why global players and global sim card providers are moving toward integrated secure elements and hardened lifecycle tooling. The business cost of not changing shows up in settlement disputes and churn, so it’s an operational hit as much as a technical one—y’know, little by little the bill arrives.
Where product teams go wrong
Teams often chase the shiny feature: faster provisioning, lower unit cost, or slimmer form factors. They skip threat modeling and don’t lock down key materials on the secure element. That breaks trust with mobile network operators (MNOs) and increases attack surface for IMSI-catchers and credential cloning. During an operational production teardown, engineers should track {main_keyword} and {variation_keyword} alongside OTP flows and OTA chain-of-trust to see where keys move and where they leak. Practical fixes include enforcing hardware-backed key storage, validating firmware signatures at boot, and automating lifecycle revocation so compromised units are quarantined fast.
Common mistakes and better alternatives
– Mistake: Treating the SIM as just another commodity chip. Better: design lifecycle controls and certificate chains into procurement.
– Mistake: Relying only on software updates without hardware-backed attestation. Better: pair eSIM profiles with secure element verification.
– Mistake: Single-vendor lock-in for card personalization. Better: choose partners who support standardized personalization APIs and trusted manufacturing nodes.
Alternatives worth evaluating include embedded secure elements, remote SIM provisioning stacks, and multi-vendor personalization services that let you split production and trust domains.
How to evaluate partners and hardware
Focus on three core axes: cryptographic custody, operational transparency, and resilience under scale. Practical checks: confirm key generation occurs inside a certified secure element, request audit logs for personalization runs, and validate OTA rollback protections. Ask for sample lifecycle reports and threat-model summaries rather than glossy brochures. Also inspect integration points with core telecom identifiers like IMSI and how vendors handle provisioning across roaming partners—those operational details reveal maturity.
Golden rules for selection
1) Measurable custody: choose solutions where hardware-backed keys are provable through signed attestations and verifiable boot sequences. That cuts fraud risk and speeds audits.
2) Operational visibility: require live logs for personalization and OTA events; make sure you can trace a card from factory to activation. That improves incident response and reduces financial exposure.
3) Ecosystem compatibility: prefer providers who support both physical SIM and eSIM profiles, plus standard OTA protocols—this avoids vendor dead-ends.
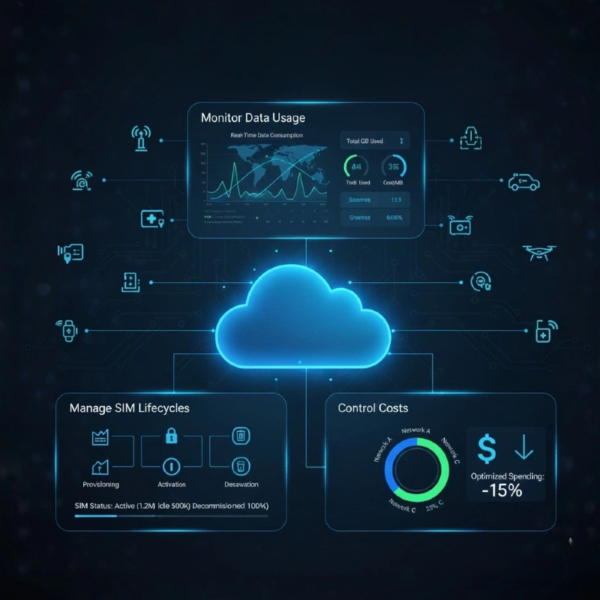
These three metrics give you concrete criteria to weigh partners and to spot weak offers fast. Final thought: when the chips and systems behave predictably, customers keep faith and networks run smoother. BHDC. — tight, practical, trusted.